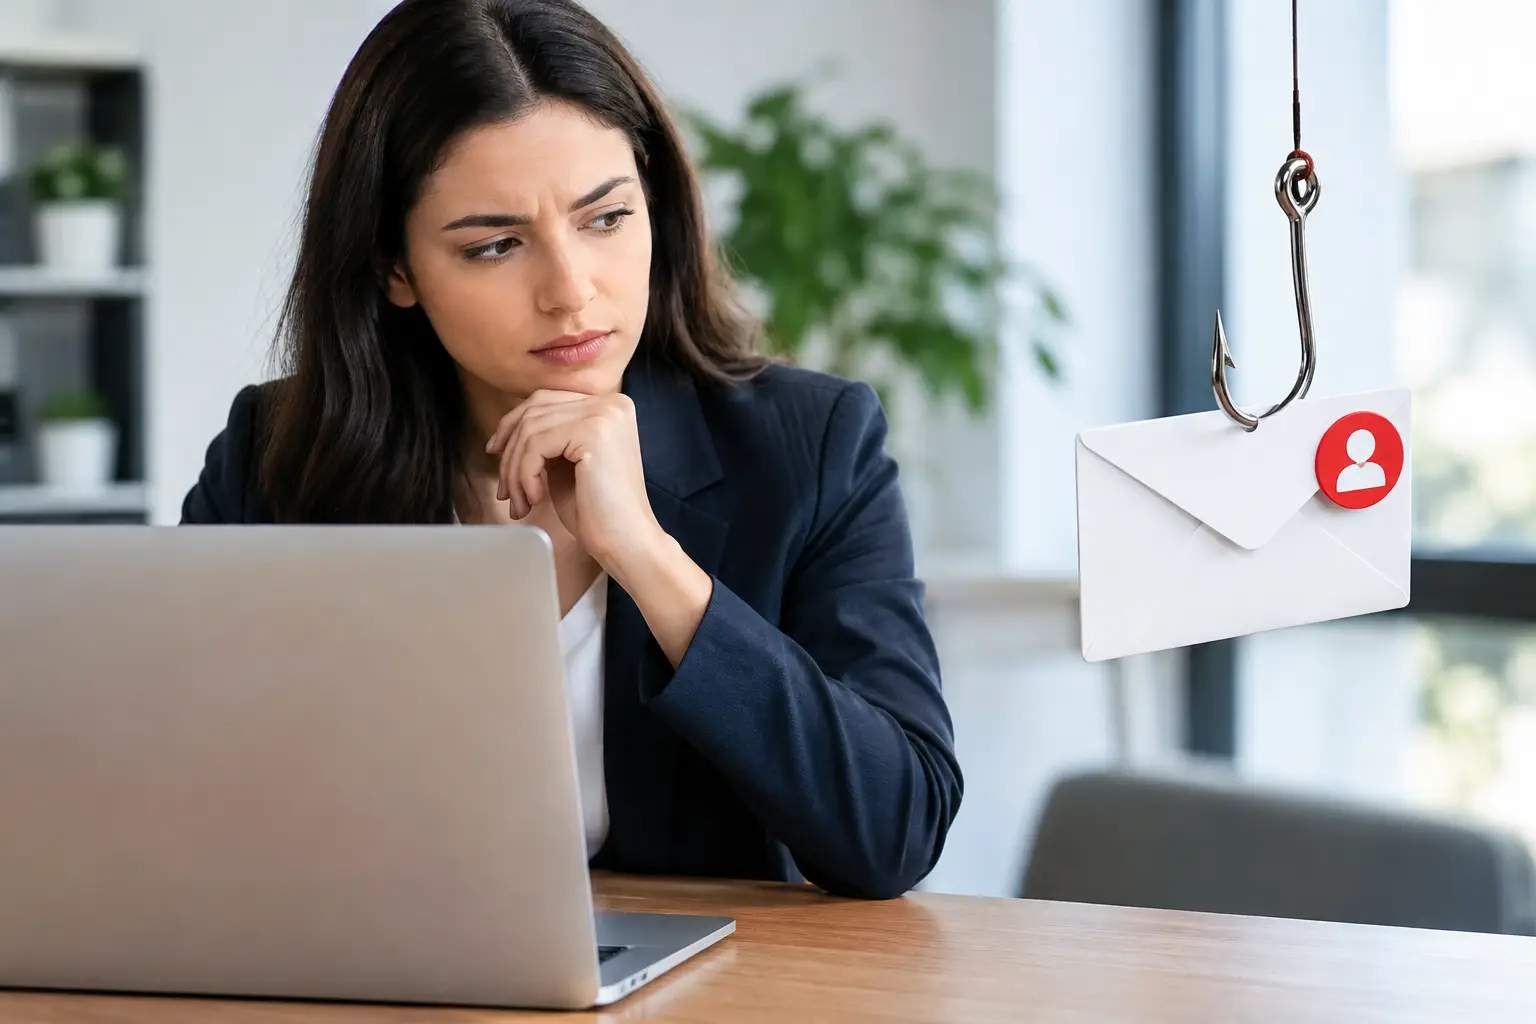
Featured Image: A professional reviewing a suspicious email beside a clear reporting workflow on screen.
By the Cyber Resilience, Risk and Business Protection Faculty 5 November 2026
A phishing incident rarely begins with a lack of intelligence or commitment. It begins with a moment of divided attention: an invoice that appears urgent, a supplier name that looks familiar, or a senior colleague seemingly requesting a quick action. To reduce phishing risk behaviours, organisations must design for those moments rather than merely remind people that phishing exists.
The central challenge is behavioural. Most employees can identify obvious scams when they are asked to do so in a calm training environment. The decision changes when the message arrives between meetings, during month-end activity, or while someone is trying to resolve a customer issue. Effective cyber resilience therefore depends on clear operating habits, proportionate controls and a culture in which reporting uncertainty is treated as sound professional judgement.
Key takeaways
- Phishing risk is shaped by workload, authority cues and unclear processes, not simply by employee awareness.
- Teams need a short, repeatable pause-and-check routine for unusual requests.
- Reporting must be fast, psychologically safe and visibly acted upon.
- Simulations should reveal process weaknesses and learning needs, not function as a test of loyalty.
- Leaders need the same standards as everyone else, particularly around payment, credential and data requests.
Table of contents
- Why capable people still respond to phishing
- How to reduce phishing risk behaviours through better decision design
- Build reporting into normal work
- Use practice without creating a blame culture
- Give leaders clear governance responsibilities
- Frequently asked questions
Why capable people still respond to phishing
Phishing is a social engineering problem before it becomes a technical one. Attackers exploit ordinary workplace signals: urgency, hierarchy, familiarity, scarcity and helpfulness. A message that appears to come from a director, a client or an established technology provider can prompt action before analytical thinking has caught up.
This is particularly relevant in professional services, finance, HR, procurement and executive support functions, where staff routinely handle confidential material and time-sensitive requests. The person who responds is often trying to be efficient, responsive and trusted. Those are valuable behaviours. The objective is not to make employees suspicious of every colleague. It is to ensure that specific high-risk actions trigger a disciplined verification step.
A common failure is treating phishing as an annual compliance topic. Staff may remember broad advice such as “do not click suspicious links”, yet lack clarity about what to do when a request is plausible but slightly unusual. That gap creates inconsistent judgement across the organisation.
How to reduce phishing risk behaviours through better decision design
The most reliable approach is to reduce the number of high-consequence decisions made on instinct. Organisations should identify the actions that require verification regardless of who appears to make the request. These commonly include changing bank details, buying gift cards, sharing credentials, approving payments, disclosing sensitive data or granting access to systems.
A simple routine is effective when it is built into daily work: pause, inspect, verify, report. Pausing interrupts the reflex to respond. Inspection means checking the sender address, wording, links, attachments and context rather than relying on display names alone. Verification means using a known independent channel, such as an established telephone number or a separately initiated Teams message. Reporting ensures that the organisation can investigate and protect others.
The routine must be specific enough to use under pressure. “Be vigilant” is not an operational instruction. “Do not action a payment-detail change from an email without calling the established supplier contact” is. The latter creates consistency, provides a defensible audit trail and removes ambiguity for staff.
Technical controls remain necessary. Multi-factor authentication, email filtering, domain protections, least-privilege access and payment approval controls reduce exposure when human judgement is tested. Yet controls can create false confidence if staff assume that any message reaching their inbox is safe. The appropriate balance depends on the organisation’s risk profile, systems and regulatory obligations, but the principle remains stable: technology should support judgement, not replace it.
Build reporting into normal work
An organisation cannot learn from suspicious messages that are deleted quietly or, worse, acted upon privately. Reporting should be as straightforward as forwarding an email to a designated address or using a clearly labelled button in the email platform. Staff should know what information to include, what happens next and whom to contact if they have already clicked, replied or shared information.
The language used around reporting matters. A person who believes they will be criticised may delay disclosure while trying to resolve the issue alone. That delay can turn a contained incident into credential compromise, financial loss or wider access to systems. Leaders should state plainly that prompt reporting is the correct action, including when someone has made an error.
Visible feedback closes the loop. If the security team identifies a campaign, a brief, factual update can show colleagues what was detected and what to watch for. Avoid naming individuals or turning incidents into cautionary theatre. The purpose is organisational learning, not embarrassment.
Infographic: The four-stage phishing response
“`text UNUSUAL REQUEST | v PAUSE – Do not act on urgency alone | v VERIFY – Use a known, independent channel | v REPORT – Escalate suspicious or mistaken action quickly | v LEARN – Improve controls, guidance and practice “`
This is also where HR, IT, finance and operational leaders need shared ownership. A phishing response process that exists only within the cyber function will struggle when a message concerns payroll, recruitment data, supplier accounts or executive communications. Cross-functional clarity is part of business protection.
Use practice without creating a blame culture
Phishing simulations can be useful, but only when they are designed with integrity and intent. A simulation should test a relevant risk scenario, measure meaningful behaviours and lead to targeted learning. It should not rely on humiliation, trick staff with sensitive personal themes or treat a click as proof of incompetence.
Good practice examines more than click rates. Did the employee report the message? How quickly? Did a team follow the expected verification process? Were particular departments exposed because of their role, workload or access? These questions produce more useful insight than a single headline percentage.
Training also needs to be proportionate. Senior leaders and executive assistants may need practice in business email compromise and impersonation. Finance teams may need stronger supplier-verification controls. Client-facing teams may need guidance on fraudulent document-sharing requests. A generic module has a place, but role-based scenarios improve transfer into real work.
For organisations seeking a concise intervention, a framework-led 90-minute cyber resilience briefing can establish a shared language around judgement, reporting and accountability without removing teams from operational priorities for extended periods. The value lies in what follows: managers reinforcing the same behaviours in workflows, communications and decision-making.
Give leaders clear governance responsibilities
Leaders influence phishing risk through the conditions they create. If senior people routinely send urgent requests from personal accounts, bypass approval processes or expect immediate responses without verification, they weaken the controls intended to protect the business. The standard must apply at every level.
Governance should define who owns phishing education, who monitors reporting patterns, how incidents are reviewed and how lessons are translated into policy or system changes. Regular review should consider trends such as repeated impersonation of particular roles, payment-process exceptions, increased reporting from a department or emerging use of artificial intelligence in fraudulent communications.
The National Cyber Security Centre provides useful public guidance on recognising and reporting suspicious communications. However, external guidance cannot substitute for an internal process that employees can recall and use. Every organisation needs to convert broad advice into decisions that make sense within its own technology, escalation routes and risk appetite.
Frequently asked questions
What are phishing risk behaviours?
They are actions that increase the chance of a phishing attempt succeeding, such as clicking unknown links, sharing credentials, bypassing verification or failing to report a suspicious request.
Is phishing training enough on its own?
No. Training creates awareness, but risk reduces when awareness is supported by clear procedures, technical controls, management reinforcement and simple reporting routes.
How often should phishing awareness be refreshed?
It depends on organisational risk and change. Short, regular reinforcement is usually more effective than a single annual session, particularly after incidents, process changes or new threat patterns.
Should organisations run simulated phishing tests?
Yes, where they are lawful, proportionate and connected to learning. Simulations should improve decision-making and reporting rather than punish individuals.
What should an employee do after clicking a phishing link?
They should report it immediately using the agreed route, disconnect if instructed by IT or security, and avoid trying to investigate or correct the issue independently.
Why are senior leaders targeted by phishing attacks?
They hold authority, access and valuable information. Their identities can also be impersonated to pressure colleagues into payments, data disclosure or urgent action.
The most mature organisations do not ask employees to become amateur investigators. They give them a disciplined way to slow down at the right moment, verify what matters and raise uncertainty early. That is how secure behaviour becomes part of professional practice rather than an additional burden.

Leave a Reply